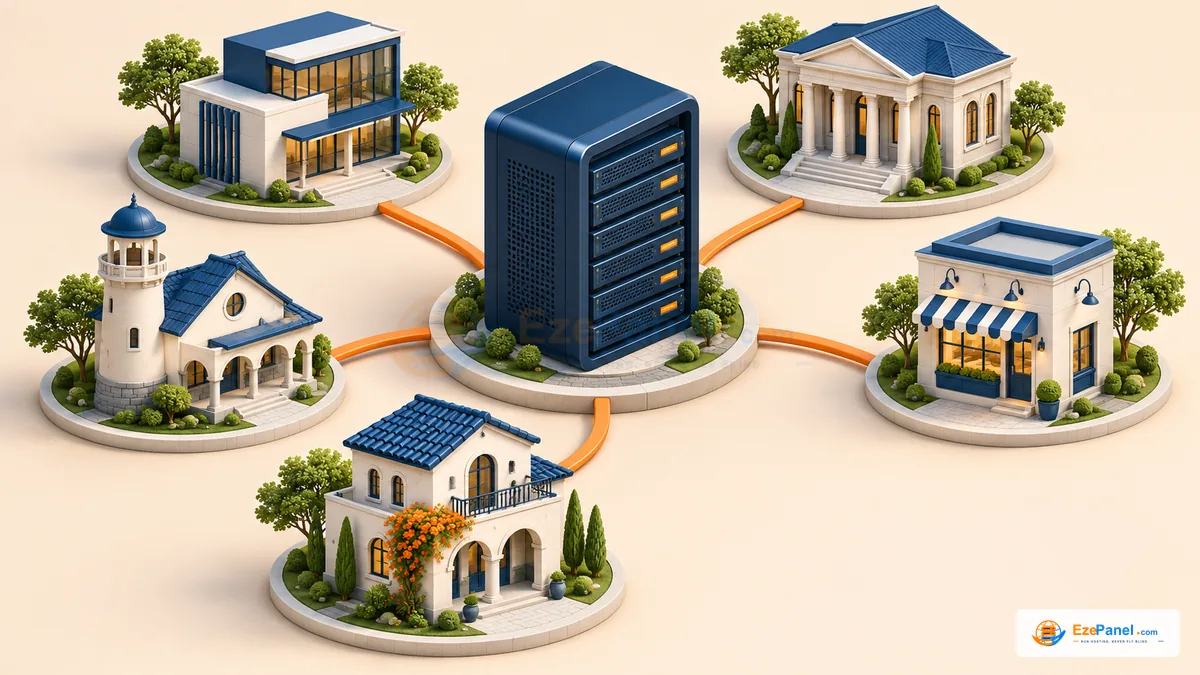
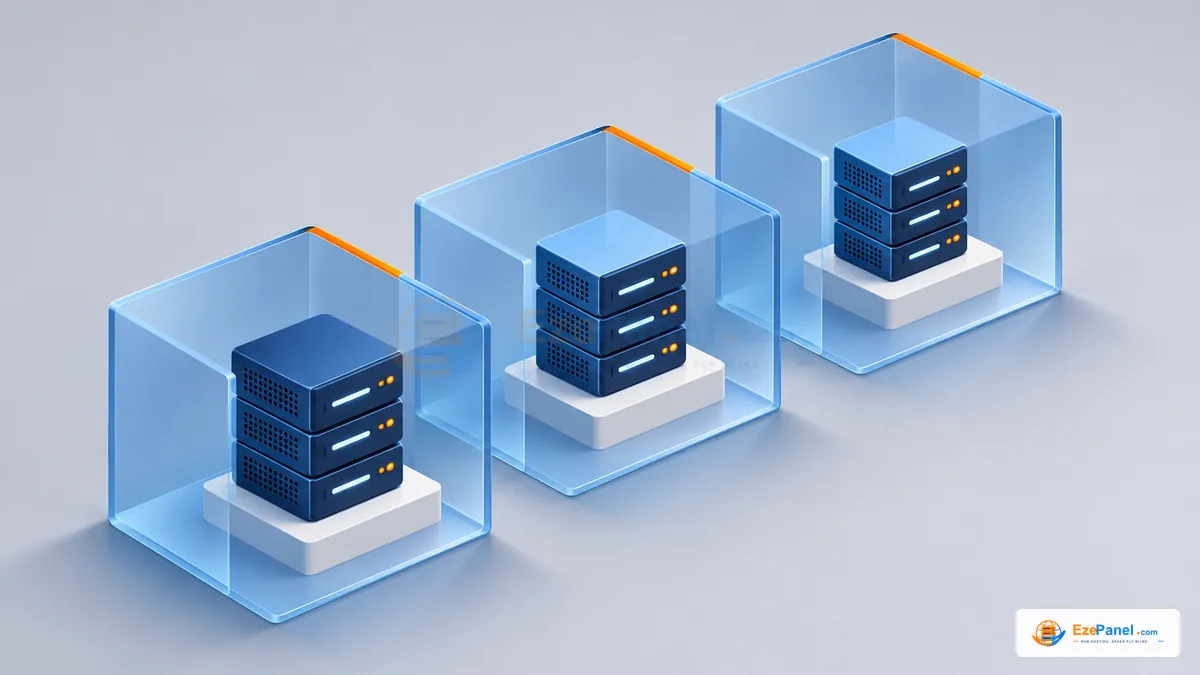
On a shared server, one busy account should not be allowed to consume resources without clear limits. Isolation starts with knowing which account owns the workload, then applying a policy that matches the service you offer.
Identity is the first boundary
Resource isolation begins with knowing who owns the workload. Files, workers and delegated actions need an accountable identity. Policy attached to the wrong owner provides little confidence about which customer a change will affect.
Separate accounts make permissions, incident attribution and restore decisions clearer. Within one account, several websites can still compete for the same account allowance. Isolation should follow the real customer boundary.
Different controls constrain different resources
CPU quotas regulate execution time. Memory boundaries constrain consumption and can cause allocation failures or process termination under pressure. Process limits constrain task creation, while PHP pool limits constrain concurrent application workers.
These controls complement each other. A cgroup is not a virtual machine, backup or guarantee against all cross-account security issues. Permissions, application behavior and shared service configuration remain relevant.
Policy must reach the workload
A saved form value does not prove enforcement. Check the effective policy, configured account slice or service, and running processes inside the intended boundary. Package defaults and overrides need to produce a predictable result.
EzePanel separates account-policy resolution from enforcement helpers and exposes related operating views. Source inspection explains this design; administrators must still verify effective limits on their installed release and host.
Map each boundary to its purpose
Separate Unix ownership, application credentials and resource policy. File permissions control access to tenant data, database grants control accessible schemas, and CPU or memory policy controls consumption. A successful check in one layer does not prove the others.
Create two disposable accounts and check the layers independently using separate sessions, database users and file paths. When an account has an override, record its effective setting rather than assuming the package name tells the whole story.
Make policy changes predictable
Record the initial policy, requested change and observed result. Test boundaries with disposable work and stop before risking other accounts. A failed operation should retain actionable information rather than silently leaving half-created resources.
Explain limits in terms customers can act on: storage allowance, allowed concurrency and how to request review. EzePanel licensing and tenant packages are distinct. Increasing software account capacity does not increase every customer’s package automatically.
Build a package policy before you onboard accounts
Write the intended entitlement and resource policy in separate columns. Entitlements govern what the customer may create; CPU, memory and PHP concurrency settings govern a different part of the operating model. A mailbox allowance should not be described as a reservation of RAM.
For a hypothetical shared VPS, start with representative account workloads and leave capacity for databases, mail and background tasks. In EzePanel, review effective package/account settings and their available runtime evidence together. If a requested controller or measurement is not available on the host, investigate that limitation before selling it as enforced isolation.
Where to go next
Sources & further reading
Official documentation for the topics in this guide. Check current vendor requirements before a purchase or server change.